Open source · AGPL-3.0 · Self-hosted
Keep your product analytics honest.
tripl keeps your tracking plan — the events, fields and values your product is supposed to send — and checks it continuously against the events that actually land in your warehouse. When the two diverge, it tells you.
No SDK. Reads ClickHouse, PostgreSQL, BigQuery, Databricks and Greenplum — with Snowflake, Redshift, Trino and Athena in preview — and never writes to it.


What you meant to track and what you actually track drift apart.
tripl is the single place where your team writes down what you intend to track, checks it against what your apps are actually sending, and gets a heads-up the moment the numbers start to look wrong.
-
Documented, but no longer arriving
A release ships and
checkout_completedquietly stops firing. The plan still lists it; the warehouse has none. -
Arriving, but never documented
New events land in the warehouse that nobody wrote down, so nobody knows what they mean or who owns them.
-
The shape changed underneath you
A field appears that you never documented, one you relied on disappears, or a field starts carrying values it never used to.
Plan. Observe. React.
Three jobs that build on each other: describe what should be tracked, watch what really arrives, and hear about it when the two stop matching.
-
Plan
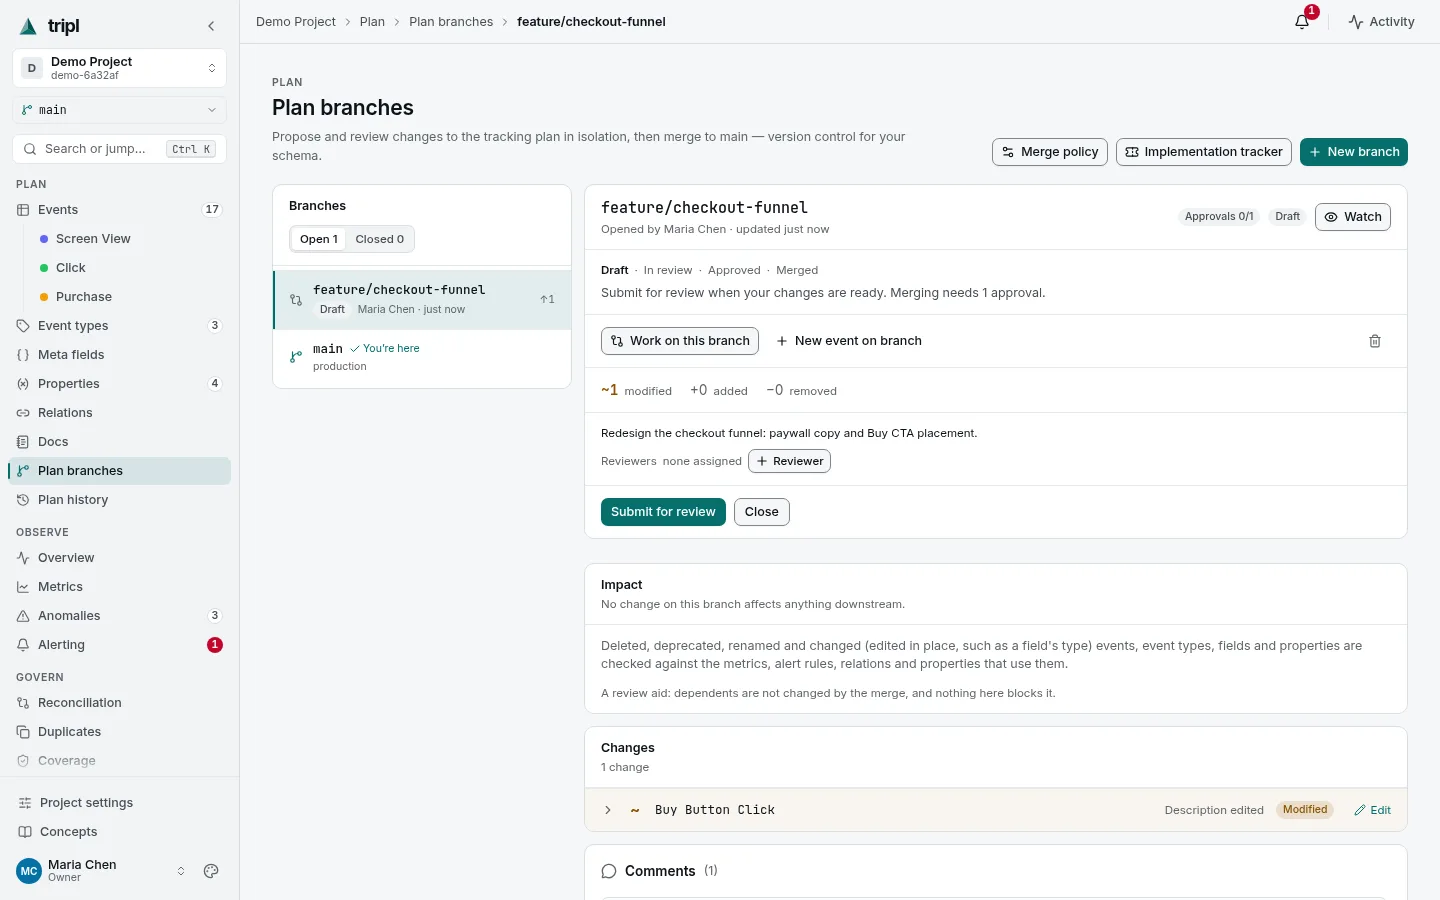
Write the plan down — and change it like code.
Every event, field and value lives in one searchable catalog. Nobody edits the main plan directly: changes go on a branch, get reviewed, and merge only when approved — like a pull request for your tracking plan.
- A diff of exactly what a branch changes
- Non-conflicting edits merge automatically; real conflicts are reported, never overwritten
- Event-type owners can gate merges that touch their types
-
Observe
Check the plan against your real data.
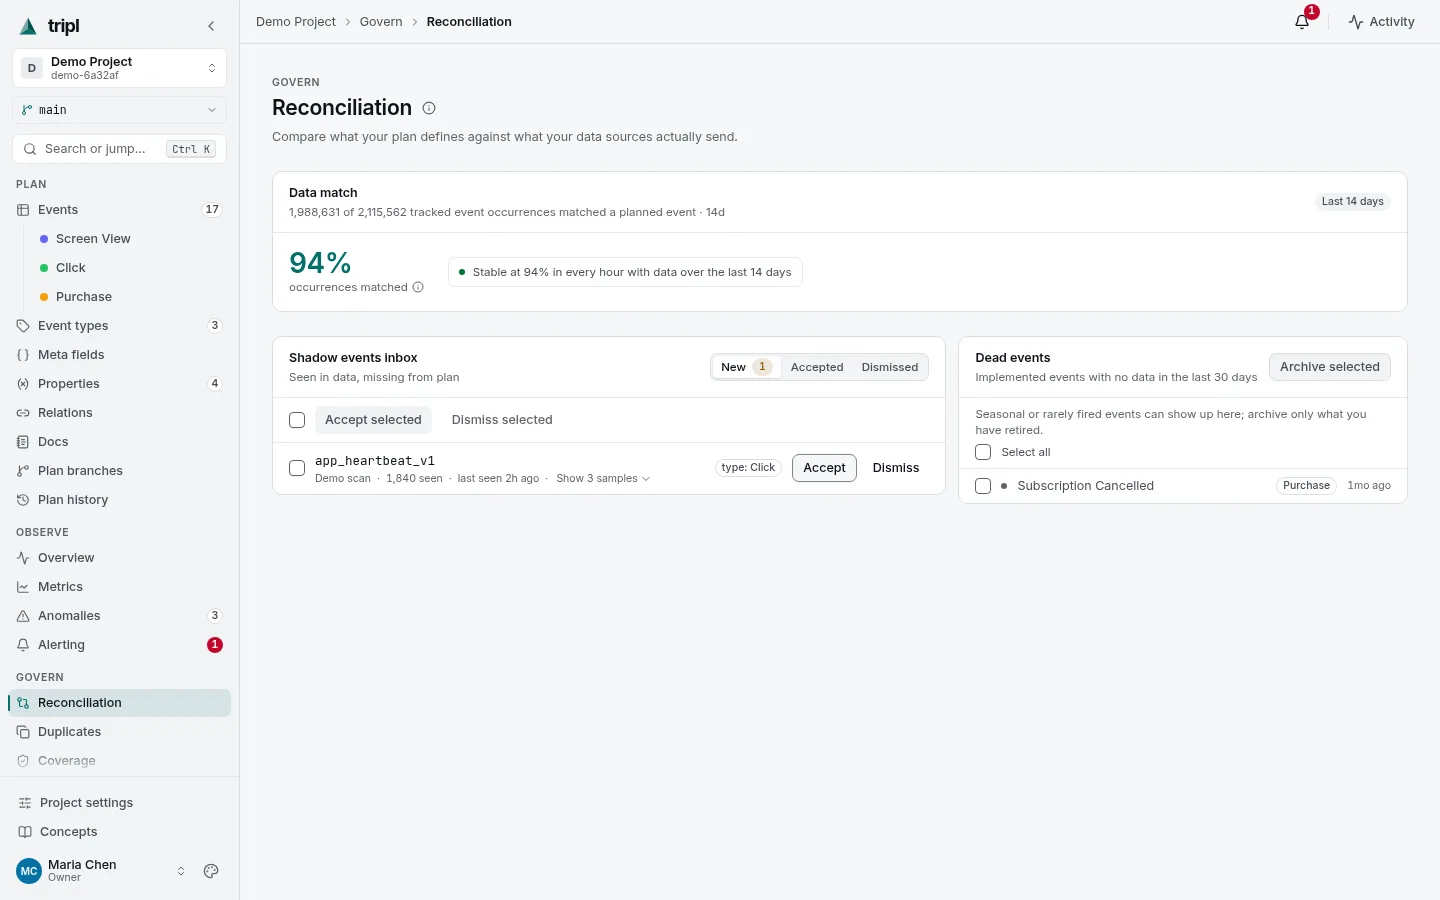
Scans read your warehouse tables and propose events, fields and value lists from what is really there — a first draft of the plan in minutes if you have none. Reconciliation then reports the gaps.
- Dead events: documented, but no longer arriving
- Undocumented events: arriving, but missing from the plan
- Monitoring scans collect volume counts on a schedule — every 15 minutes to weekly
-
React
Get told when reality drifts.
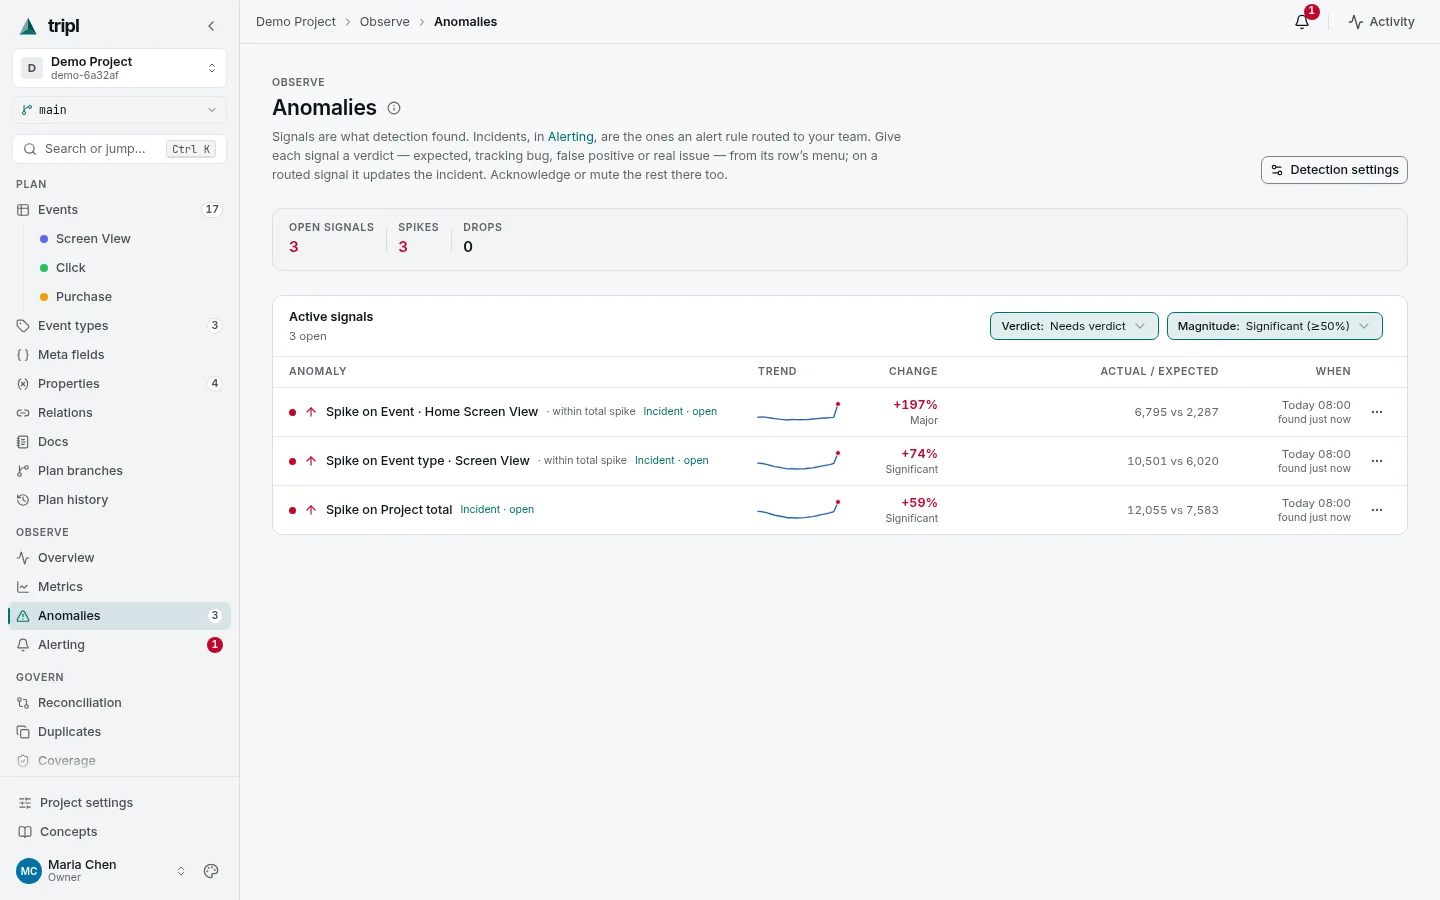
tripl learns each event's daily and weekly rhythm and raises a signal on a spike, a drop or a change in shape — with no detection to configure. Alert rules decide which signals are worth interrupting someone for, and where they go.
- Every signal broken down by the slice of data that moved
- A simulator replays recent days against a rule before you switch it on
- Cooldowns so one problem does not page you over and over

Everything between the plan and the warehouse.
-
One catalog
Every event, field and value in one searchable place, with types, owners and lifecycle status.
-
Branches and review
Change the plan on a branch, review the diff, merge when approved. Main is never half-finished.
-
Scans that draft the plan
Point a scan at a warehouse table and it proposes events, fields and value lists from real data.
-
Seasonal anomaly detection
Baselines that learn each event's daily and weekly rhythm flag spikes, drops and shape changes.
-
Why it changed
Each signal is broken down by the slice that moved — platform, country, plan — not just a red number.
-
Schema and value drift
New, missing or retyped fields, and values outside a property's documented list, surfaced per event.
-
Release regressions
An event that disappeared or fired far less in the newest app version than in the one before it.
-
Alerts where your team works
Slack, Microsoft Teams, Telegram, PagerDuty, email, webhooks, Jira and Linear — with cooldowns, templates and a delivery history.
-
Roles, audit log, API keys
Viewer, editor and owner roles, a log of every change, and scoped, revocable keys for scripts and agents.
Your agents read the plan. Your CI enforces it.
One searchable source of truth — for people in the app, for scripts through the API, and for LLM agents through MCP.
-
Search that understands the plan
Ctrl+K searches the whole plan and your team's notes with fuzzy matching, no setup needed. Point it at any OpenAI-compatible embeddings endpoint — including one you host — and results rank by meaning, not spelling.
AI and search -
A first-party MCP server
tripl-mcp gives any MCP client typed tools to search the plan, read events, fields and notes, check open signals and propose changes — on a branch, never straight to main by default. A read-only key keeps an agent to looking.
Connect an AI agent$ uvx tripl-mcp -
tripl check in CI
Catch a misspelled event or an undocumented value in the pull request, not in the warehouse a week later. Scan tracking calls in source or validate captured payloads; SARIF output feeds code scanning.
tripl check$ uvx tripl check --format sarif > tripl-check.sarif -
Typed tracking code
tripl codegen writes Swift, Kotlin and TypeScript from the plan, so a wrong value is a compile error in Xcode, Android Studio or tsc — with autocompletion for every value the plan allows.
tripl codegen$ uvx tripl codegen --check
Everything else goes through the same REST API: an OpenAPI contract, scoped and revocable
read-only or read-write keys, and the tripl CLI's doctor, status and
watch for the instance itself.
No SDK. Your warehouse, read-only.
tripl reads the analytics events already landing in your warehouse — nothing to ship, nothing to re-instrument. It never writes to the warehouse, and it stores only the aggregated counts it needs, never your raw events.
Snowflake, Amazon Redshift, Trino and Amazon Athena are in preview: their connectors have not yet passed the value suite against a live warehouse (proven versus believed).
- ClickHouse
- PostgreSQL
- BigQuery
- Snowflake , Preview
- Databricks
- Amazon Redshift , Preview
- Greenplum
- Trino , Preview
- Amazon Athena , Preview
Runs on your infrastructure. Your data stays in your warehouse.
The server and web app are licensed under the GNU AGPL v3.0; the CLI and the MCP server
under Apache 2.0. tripl ships as one image, published for linux/amd64 and linux/arm64.
Try it locally
Docker and about fifteen minutes. Create the first account and click Generate demo project — no warehouse needed.
$ git clone https://github.com/tripl-io/tripl.git
$ cd tripl
$ cp .env.example .env
$ docker compose -f compose.dev.yaml up --build
# then open http://localhost:5173Deploy for your team
One command writes the production stack, generates its secrets and starts it. uv is the only thing
to install on the host.
# pin a released tag with --version X.Y.Z; --dry-run first
$ uvx tripl install \
    --app-url https://tripl.example.com \
--dir /srv/tripl- Read-only access to your warehouse
- One anonymous ping a day in Community, off with
TELEMETRY_ENABLED=false(what it sends) - Source on GitHub
Find out what your analytics are really sending.
Clone the repository and generate the demo project: a complete project on a local synthetic warehouse, where real scans, metric collection, anomaly detection and reconciliation run — no warehouse needed.